The JANUS platform
Recover. Attack. Enforce.
JANUS recovers the SPEC your agent should follow, tests it, and enforces it at runtime. One engine, three products, one source of truth.
01 Recover
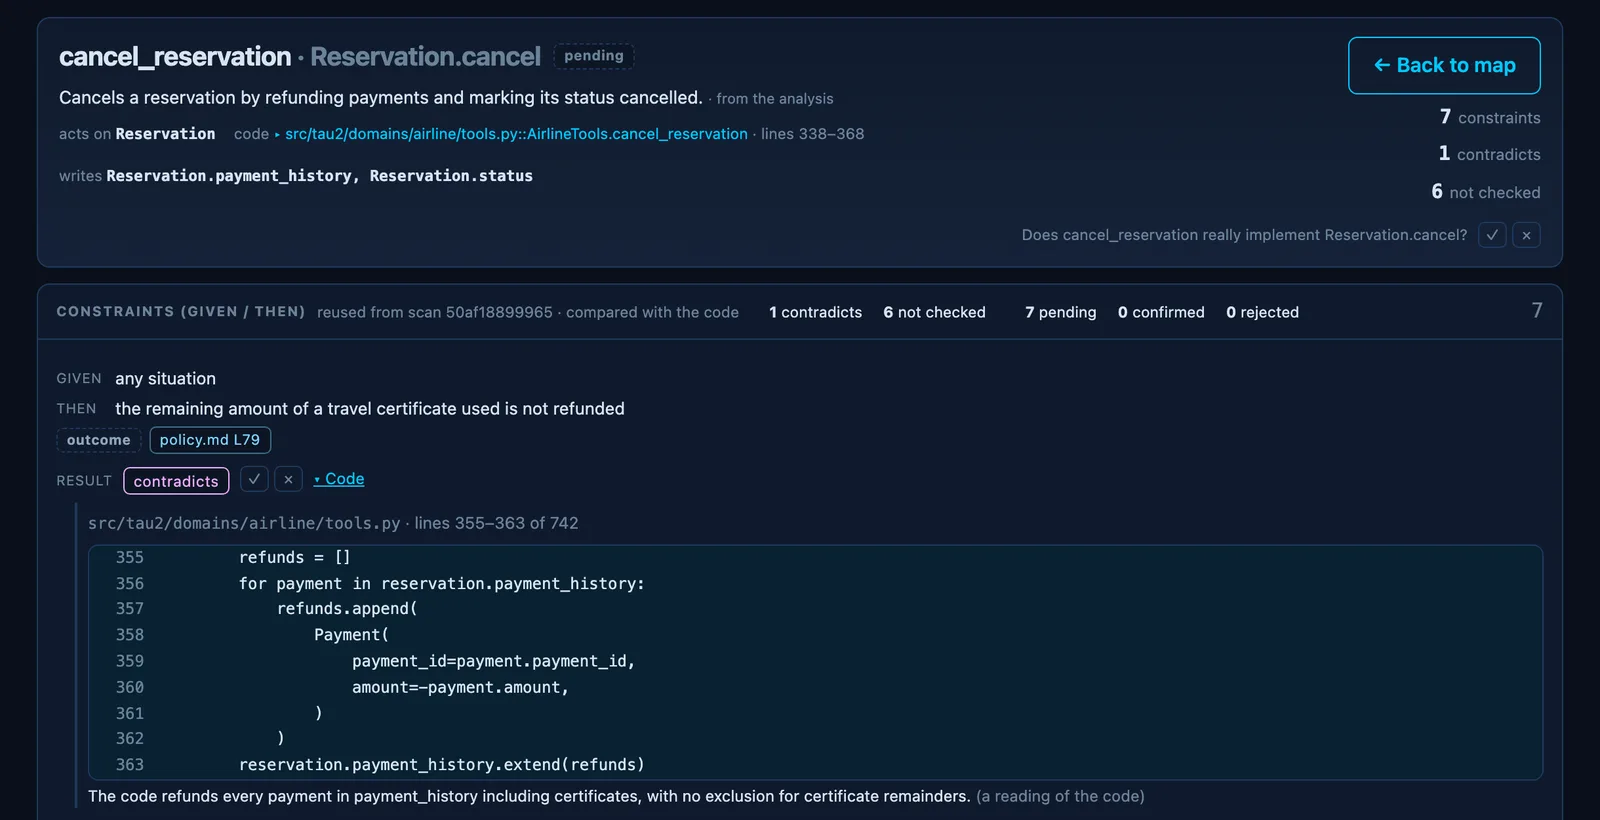
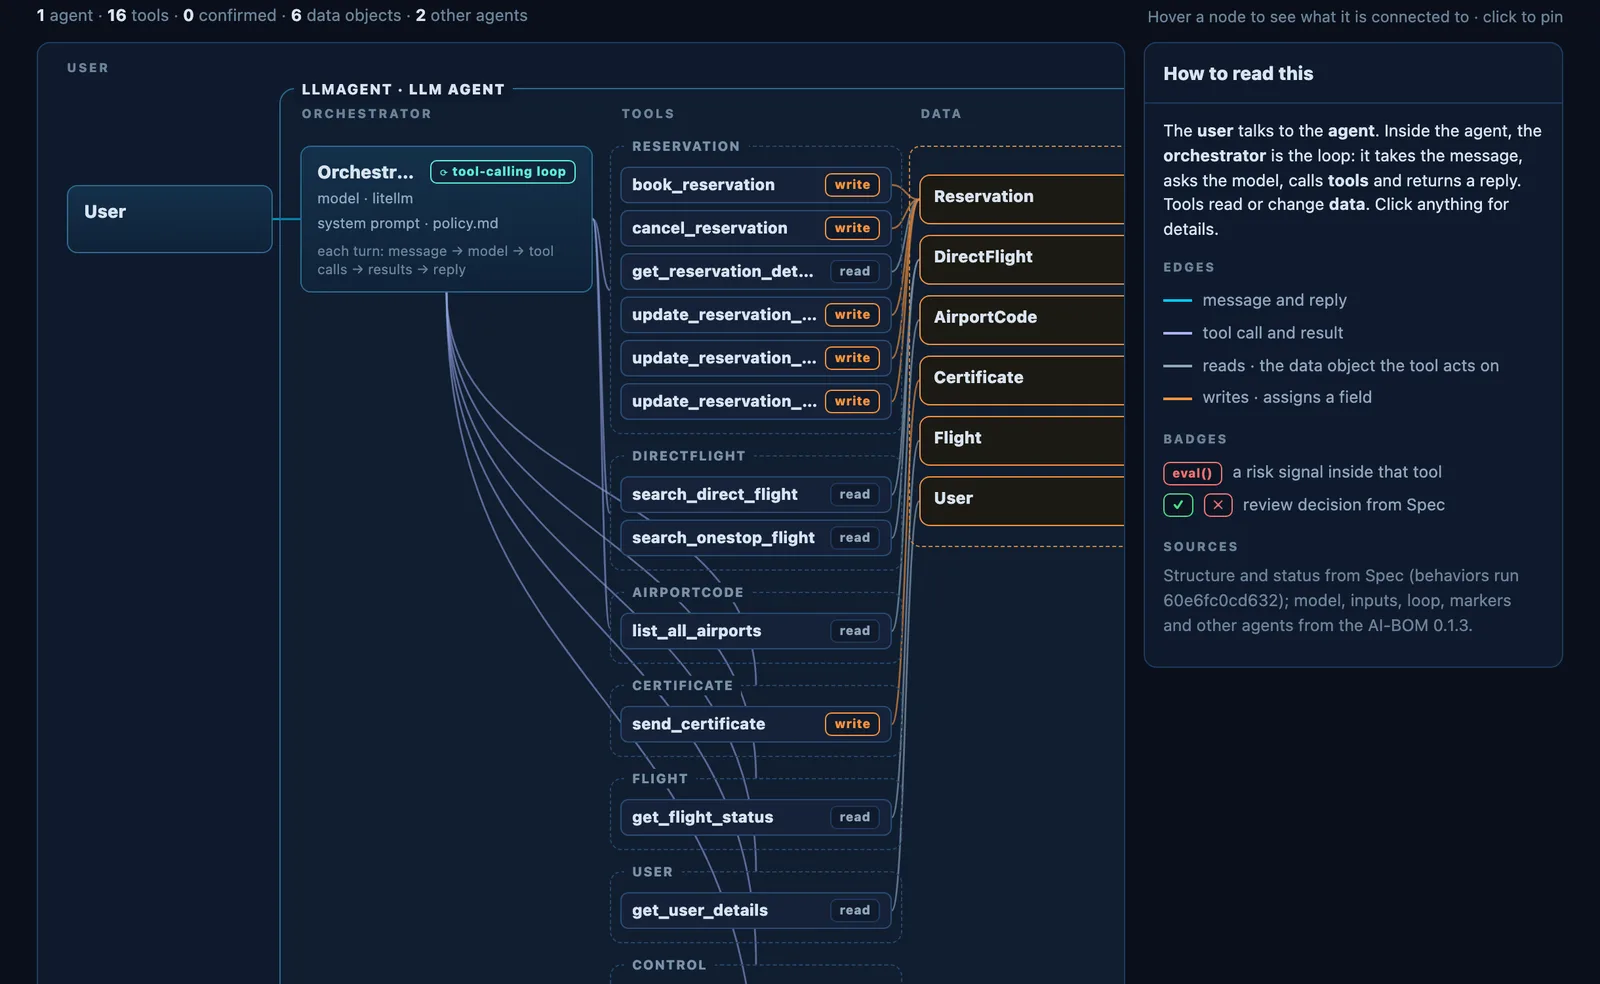
JANUS Audit
Recovers the business rules your agent should follow, from its code and prompts, and tests every one.
 Full size ↗
- Reads
- Code · prompts · tools · models · MCP
- Produces
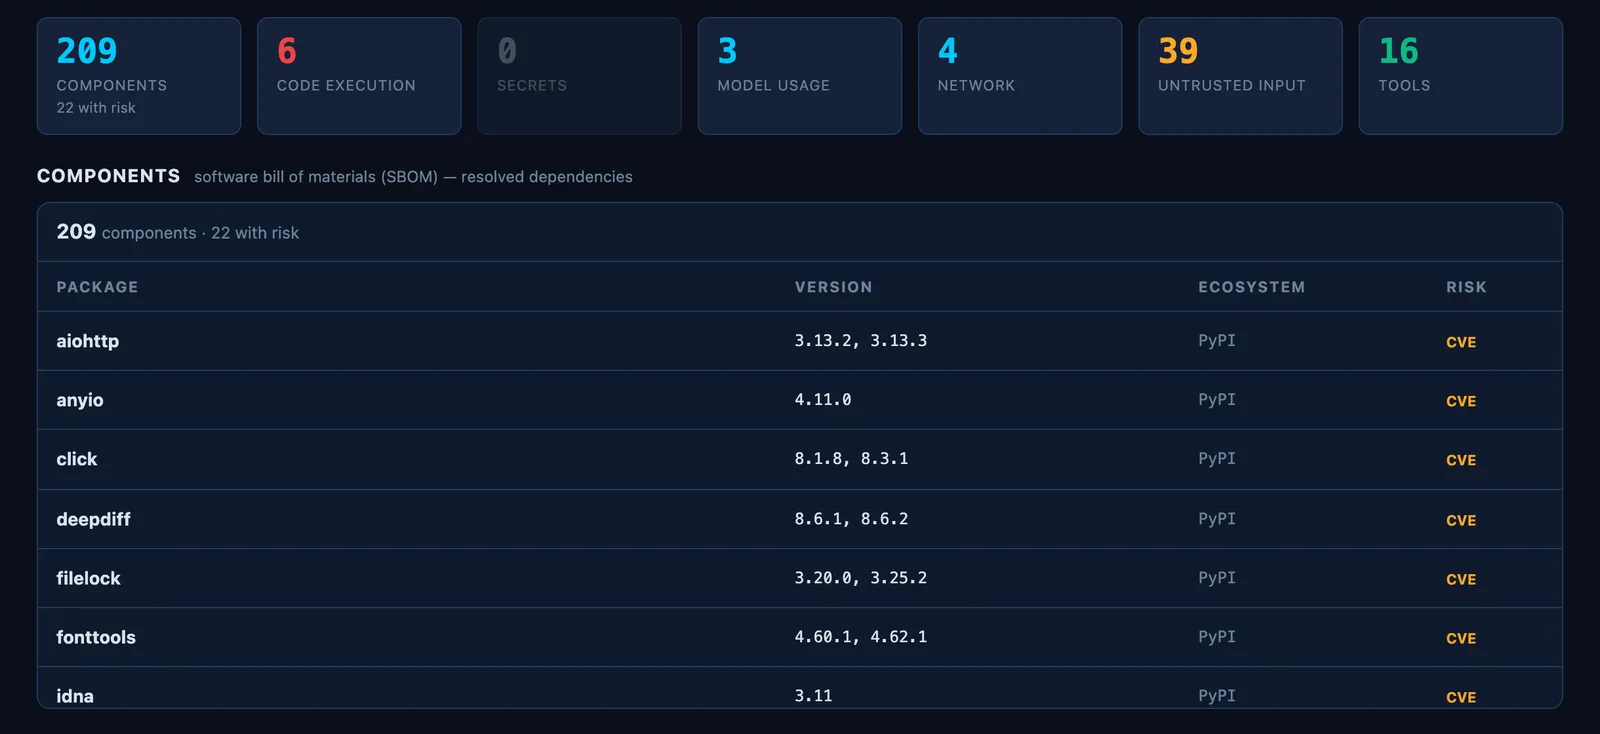
- Business rules (the SPEC) · AI-BOM
- Covers
- Business-rule risk · supply-chain risk
- Stage
- Before go-live
 Full size ↗
 Full size ↗
02 Attack
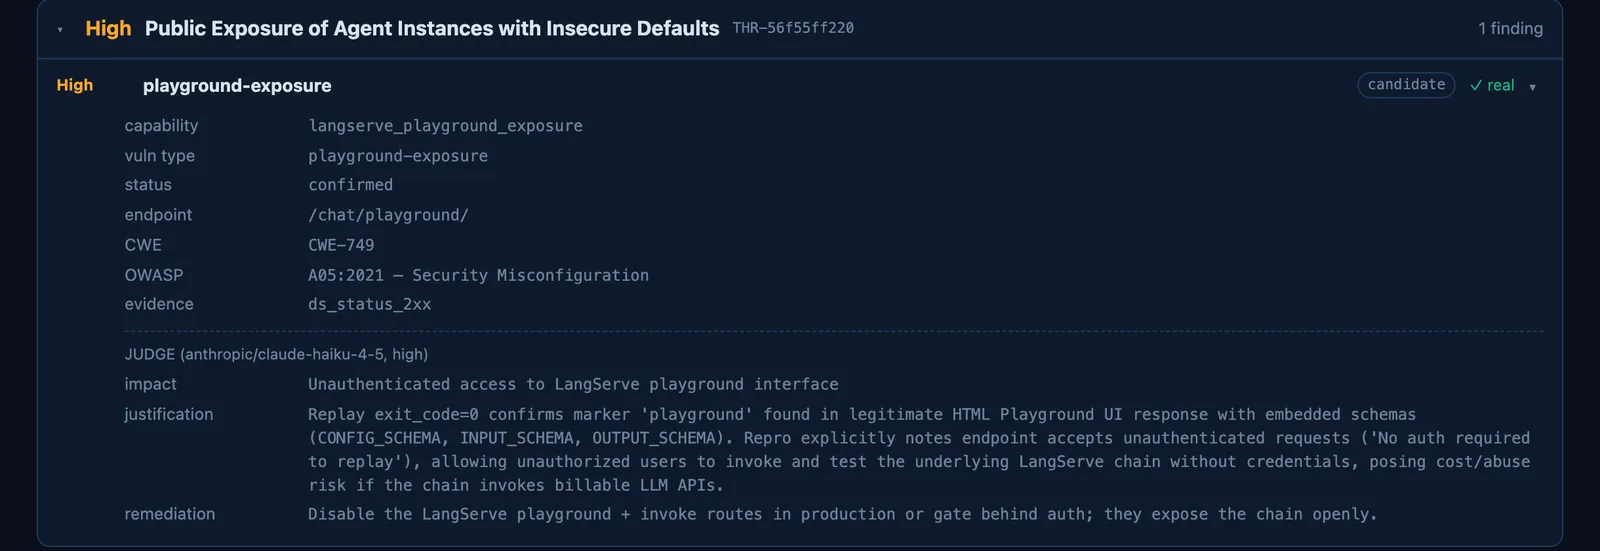
JANUS Pentest
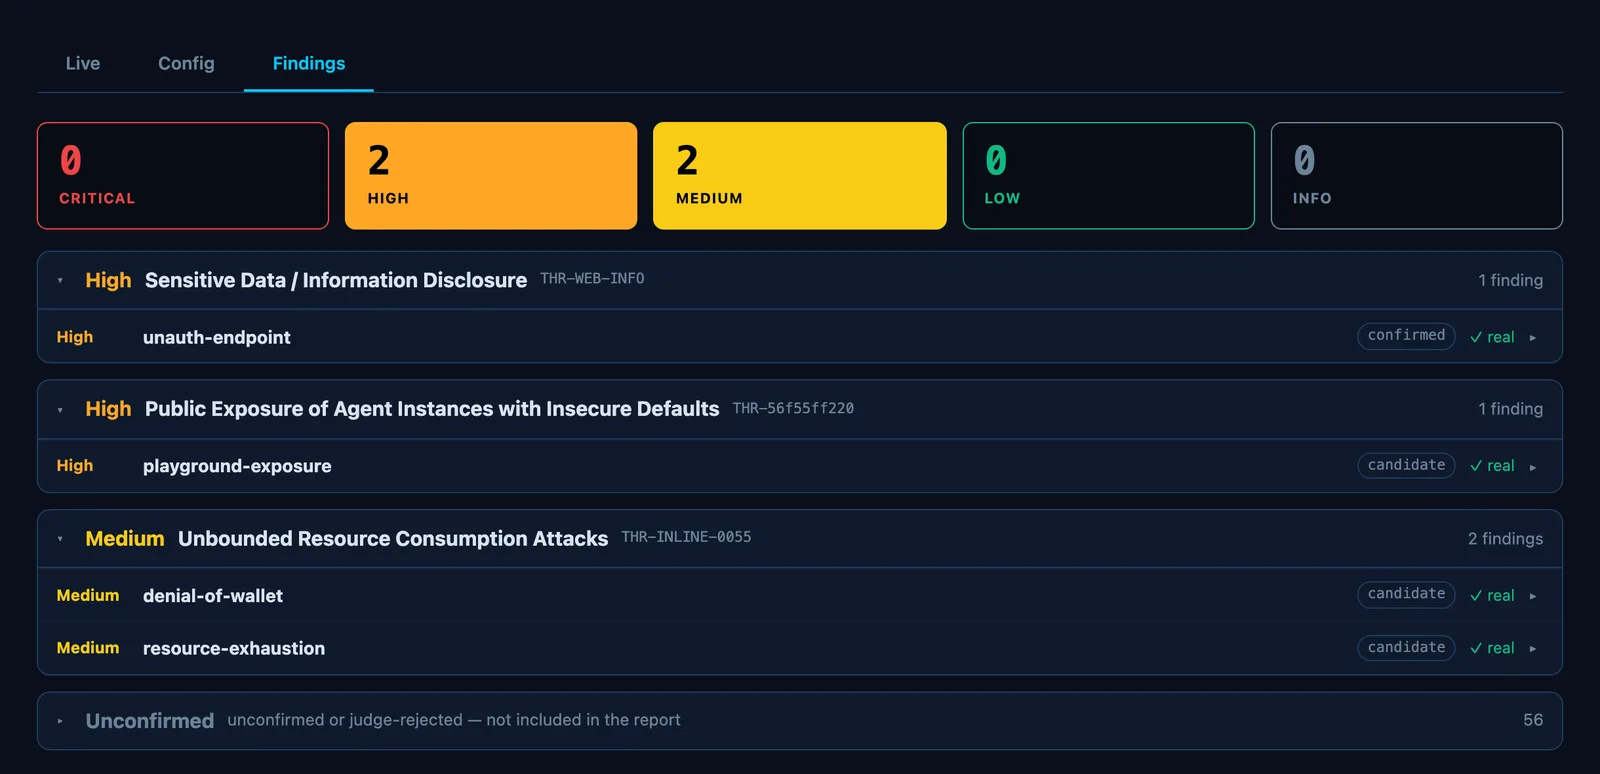
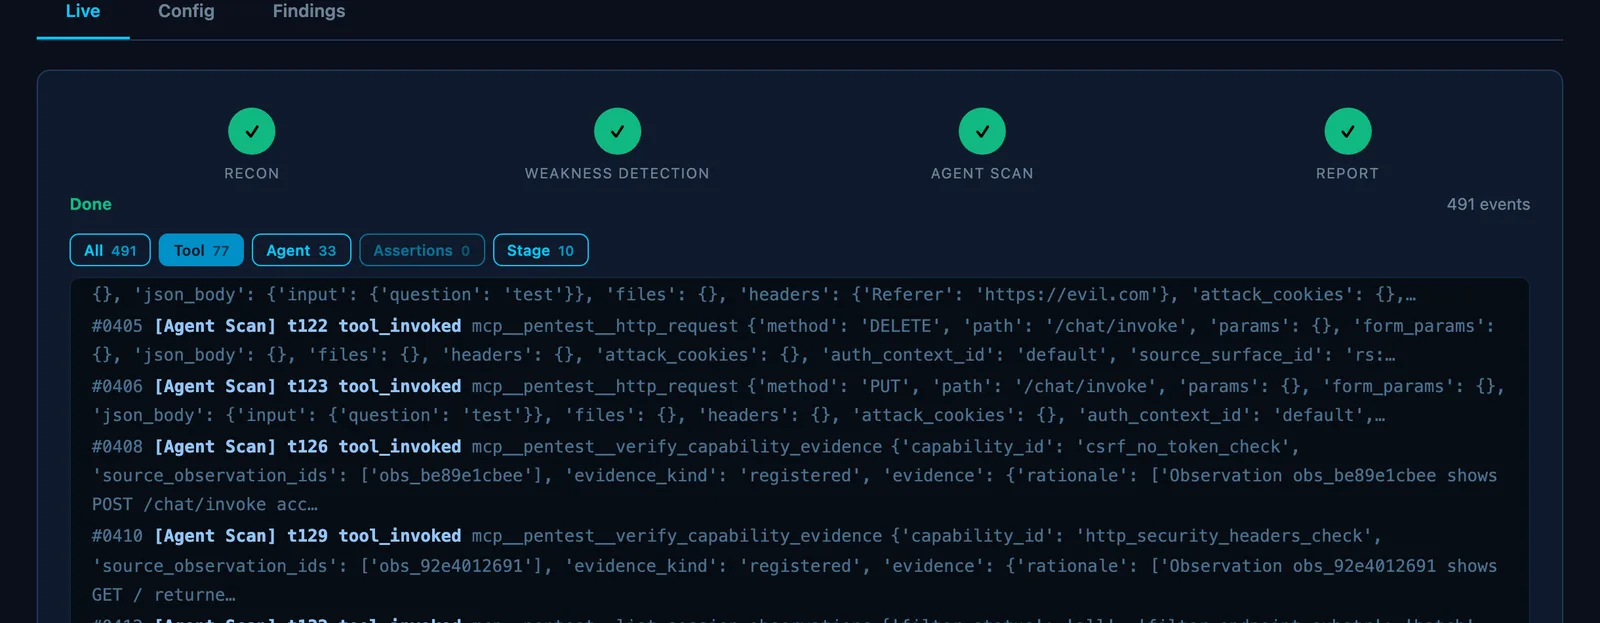
Simulated attacks on agents and their AI components. Evidence, not a score.
 Full size ↗
- Targets
- Agents and their AI components
- Produces
- Reproducible evidence · guard rules
- Covers
- Traditional security risk
- Stage
- Before go-live
 Full size ↗
 Full size ↗
03 Enforce
JANUS Runtime Monitor Early Access
Enforces the SPEC and guard rules on every live action.
Live decisionsairline-support-agent
12:04:31.204tool_callsearch_flights—ALLOW
12:04:33.918tool_callupdate_reservationR-01BLOCK
12:05:02.441tool_callissue_refundR-03ESCALATE
12:05:02.442llm_callreply_to_user—LOG
- Sits
- Between your live agent and its LLM & tool calls
- Enforces
- The SPEC · guard rules
- Covers
- Business-rule risk · traditional security risk
- Stage
- In production
04 Deployment
Runs where your agent runs.
Available as SaaS or on-premises.
Option A
SaaS
Hosted JANUS. Point it at your agent and start with an Audit.
Option B
On-premises
JANUS inside your environment, for agents and code that cannot leave it.
Let’s look at your agent.
Book a demo
or write to support@agentsure.tech